The End of 45-Minute Screenshares: How the ZeroTrust Forensic Scanner Catches What In-Game Anticheats Miss
In-game anticheats only see what happens inside the game process. The ZeroTrust Forensic Scanner reads memory, driver signatures, and system artifacts directly—giving server owners irrefutable proof in under 60 seconds without invasive screensharing.
Every FiveM server owner, competitive tournament organizer, and head administrator knows the exhausting routine: a player is reported for impossible aim or unnatural movement, your in-game anticheat doesn't have an instant signature for their private $50/month cheat loader, and your staff is forced to drag the suspect into a chaotic Discord voice channel for a 45-minute manual screenshare.
- It wastes massive staff hours: Moderators spend 30 to 60 minutes manually digging through Prefetch folders, Process Hacker, BAM registries, and event logs.
- It is easily bypassed: Modern private cheats use USB loaders, unlinked memory routines, string cleaning, and self-destruct hotkeys to wipe traces before staff even connect.
- It violates player privacy: Forcing players to open personal folders, browser histories, and private Discord messages creates friction, hostility, and massive community drama.
The ZeroTrust Solution
Why in-game anticheats aren't always enough
- Stealth Memory Mappers & Loaders: Cheats inject directly into active game memory and immediately delete their original binaries from the disk.
- Vulnerable Signed Drivers (BYOVD): Attackers abuse legitimate signed Windows drivers to gain kernel privileges and manipulate game memory without tripping basic OS security.
- Unlinked Process Threads & Hidden Modules: Tools like Eulen, RedEngine, TZX, and Gosth frequently use custom hooking techniques that operate outside standard game script telemetry.
To catch these elusive tools, you cannot rely solely on in-game script hooks. You need a dedicated, system-level forensic check that inspects memory regions, running process trees, and kernel drivers directly at runtime.
How it works: 3-step zero-friction workflow
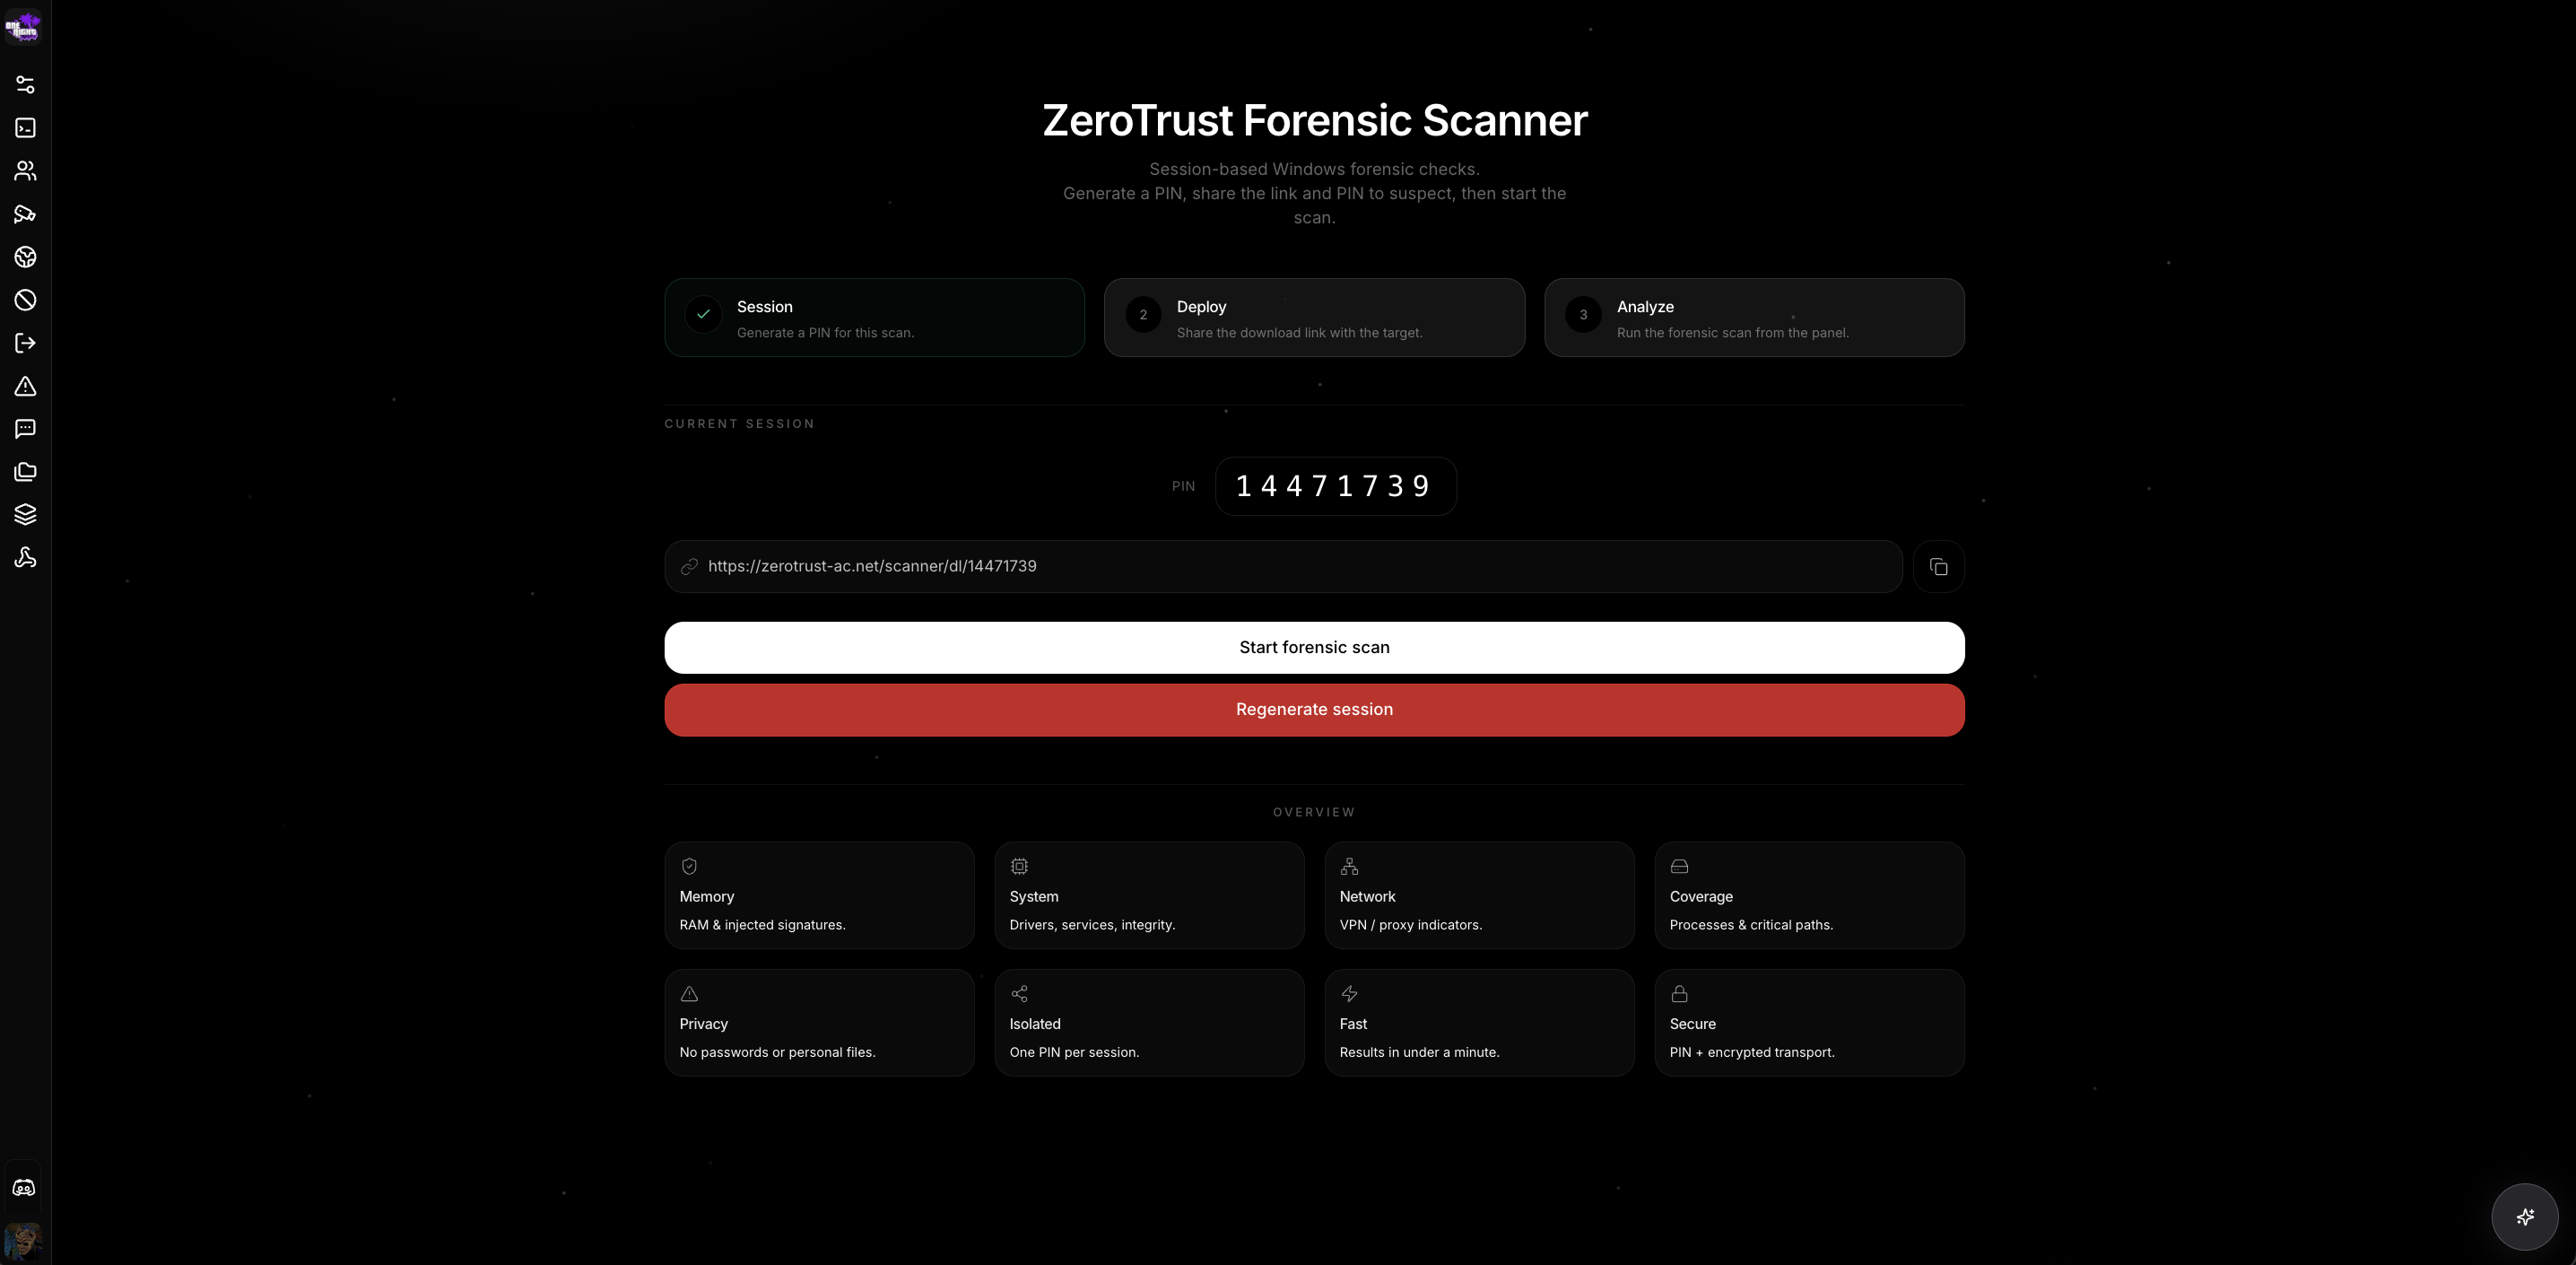
- Generate an Isolated Session: From the ZeroTrust dashboard, click New Session. The system generates a single-use 6-digit PIN and an encrypted download link (`zerotrust-ac.net/scanner/dl/[scanId]`).
- The Player Runs the Scanner: The suspect downloads the lightweight, standalone executable (no installation required) and types in the session PIN.
- Automated Verdict in Under 60 Seconds: The scanner performs its deep inspection routines, streams telemetry to your live dashboard, and categorizes findings into Good, Warning, and Severe lanes with a clear integrity verdict.
Deep technical capabilities: what the scanner analyzes
1. Direct memory analysis & injected DLLs
The scanner inspects active memory allocations, thread call stacks, and unlinked modules. Even if a cheat loader deletes itself from the hard drive the instant it injects, its in-memory signature and hooked virtual addresses remain visible.
2. Windows execution artifacts (Prefetch, BAM, Amcache & ShimCache)
- Prefetch & BAM (Background Activity Moderator): Tracks recent process executions, timestamps, and execution counts—even if the `.exe` was renamed or launched from a hidden temp folder.
- Amcache & ShimCache: Captures SHA-1 hashes, file paths, and compilation headers of previously executed programs.
- PCA (Program Compatibility Assistant): Identifies loader remnants and compatibility-shimmed utilities.
3. Signed drivers & kernel integrity
Advanced FiveM bypasses frequently rely on Bring Your Own Vulnerable Driver (BYOVD) attacks to disable anticheat callbacks. The ZeroTrust scanner verifies driver certificates, checks against blacklisted vulnerable drivers, and detects unsigned kernel hooks.
4. Anti-forensics & tampering detection
- Clearing Windows Event Logs (`EVTX`)
- Disabling diagnostic services (`DiagTrack`, `PCAsvc`)
- Recent Recycle Bin modifications and USN Journal wiping
- Virtual Machine environments (VMware, VirtualBox, QEMU) and HWID spoofers
5. Hardware snapshot & alt evasion tracking
Every scan records an immutable hardware snapshot (CPU, Motherboard UUID, Storage Serials, RAM layout, OS build). If a banned player creates a new Discord or FiveM account to evade punishment, their hardware identifiers link them back immediately.
Privacy by design: hard proof without invasiveness
- ❌ No personal files, documents, or photos are accessed or uploaded.
- ❌ No passwords, cookies, or browser tabs are read.
- ❌ No persistent agent stays on the player's computer—it runs once and closes cleanly.
- ✅ Only game-integrity, driver, and execution artifacts are evaluated.
Cross-server intelligence: the Finder System
Cheaters rarely stay on just one server—they hop from community to community until they get caught again. Every scan completed with ZeroTrust updates our Finder System. When you review a suspect, you can instantly see their global pass/fail history, linked alt accounts, and previous scan logs across all participating ZeroTrust servers.
Built directly into ZeroTrust (no seat tax)
Unlike standalone screenshare tools that charge expensive monthly subscriptions or impose a 'seat tax' per staff member, the Forensic Scanner is built directly into the ZeroTrust Cloud Panel and included with the Lifetime License. Instant Discord webhook alerts keep your entire moderation team in sync in real time.